A website is more than a digital presence.
For many businesses, it is a place where customers interact, services are delivered, and important information is exchanged.
Customers submit inquiries.
Users create accounts.
Businesses process transactions.
Employees manage online systems.
Because websites handle valuable information, they have become common targets for cyber attacks.
Many security incidents do not happen because of advanced hacking techniques. They happen because of simple weaknesses that remain unnoticed.
Understanding common website vulnerabilities helps businesses take preventive action and create a safer online environment.
Outdated Software Creates Security Risks
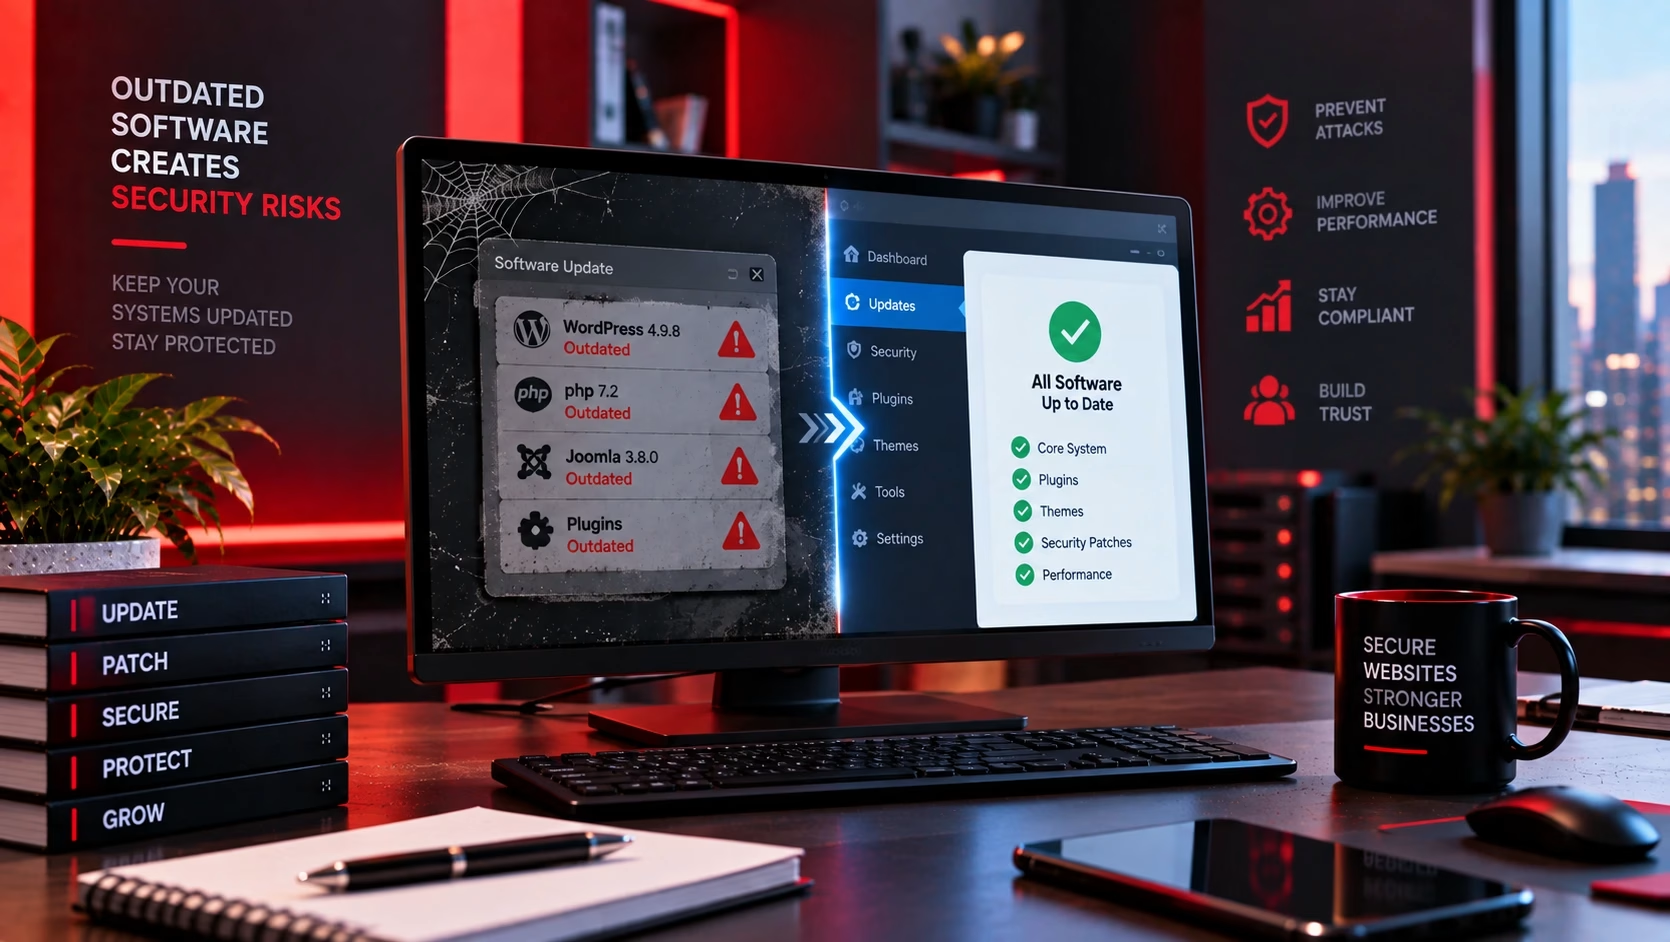
One of the most common website security problems is outdated software.
Websites often depend on multiple components.
Content management systems.
Themes.
Plugins.
Frameworks.
Server applications.
Developers regularly release updates to improve functionality and fix known security issues.
When businesses delay these updates, attackers may exploit existing vulnerabilities that have already been identified.
Regular maintenance and timely updates are essential parts of website protection.
Businesses can also explore additional website security measures to protect their online presence and understand how preventive practices help reduce exposure to common threats.
Weak Passwords Allow Unauthorized Access
Passwords remain one of the simplest security layers.
They are also one of the most commonly targeted.
Weak passwords.
Reused passwords.
Shared login credentials.
These practices increase the risk of unauthorized access.
Businesses should encourage strong password policies and use additional security measures such as multi-factor authentication.
Limiting administrator accounts also reduces unnecessary exposure.
Poor Access Management Increases Risk
Not every user needs complete website control.
However, many businesses provide more access than necessary.
For example, a content writer may not need administrator-level permissions.
A temporary employee may not need permanent access.
Poor access management creates opportunities for misuse or accidental changes.
Businesses should follow the principle of least privilege by giving users only the permissions required for their responsibilities.
Lack of SSL Protection Affects Trust
Website visitors expect secure connections.
When websites do not use HTTPS, customer information may be exposed during transmission.
An SSL certificate enables encrypted communication between the user’s browser and the website server when HTTPS is configured correctly.
It helps protect:
- Login details
- Contact information
- Payment data
- Submitted forms
SSL is not a complete security solution, but it is a fundamental requirement for modern websites.
Businesses looking to understand encryption and secure connections can learn more about why SSL certificates are essential for website security.
Vulnerable Plugins and Extensions
Many websites use third-party tools to add functionality.
Plugins can add features.
Themes can improve design.
Extensions can connect external services.
However, poorly maintained or vulnerable plugins can create security weaknesses.
Businesses should install software only from trusted sources, remove unused plugins, and keep active components updated.
Regular reviews help reduce unnecessary risks.
Inadequate Backup Practices
Backups do not prevent attacks.
They help businesses recover after problems occur.
Without reliable backups, a security incident can result in permanent data loss.
A strong backup strategy should include:
- Regular backup schedules
- Secure storage locations
- Recovery testing
A backup is valuable only when the business can successfully restore the website when needed.
Malware Infections and Malicious Code
Attackers may insert malicious code into websites for different purposes.
They may redirect visitors.
Steal information.
Send spam.
Create hidden access points.
Sometimes these infections remain unnoticed for long periods.
Regular security scanning and monitoring help identify suspicious activity earlier.
If a website has already been compromised, businesses need to identify the source of the infection, remove malicious files, and secure affected accounts.
Understanding how to fix a hacked website and improve website security can help businesses plan the recovery process and reduce the risk of repeated attacks.
Server Configuration Weaknesses
Website security depends not only on the website itself.
The hosting environment also matters.
Poor server configurations can create vulnerabilities.
Examples include:
- Incorrect file permissions
- Unprotected services
- Weak security settings
- Missing updates
A secure hosting environment provides an important foundation for protecting websites.
Lack of Security Monitoring
Many businesses discover security problems after customers report them.
By that time, the damage may already be significant.
Continuous monitoring helps identify unusual activity earlier.
Businesses can monitor:
- Login attempts
- File changes
- Traffic patterns
- Security alerts
Early detection allows faster response and reduces potential impact.
Human Mistakes Remain a Major Factor
Technology alone cannot prevent every security issue.
Employees may accidentally:
- Open malicious attachments
- Share credentials
- Download unsafe files
- Ignore security warnings
Security awareness training helps employees understand common risks and make safer decisions.
A security-conscious team becomes an important part of website protection.
Building a Stronger Website Security Approach
Website security requires multiple layers working together.
Businesses should combine:
- Regular updates
- Strong authentication
- Secure hosting
- Backups
- Monitoring
- Access controls
No single tool can protect against every threat.
A complete security approach reduces risks more effectively.
Businesses seeking professional website security in Pakistan can explore solutions that combine vulnerability assessment, malware protection, monitoring, and recovery support to strengthen their website defenses.
Where Chromeis Fits
Chromeis helps businesses protect their websites through comprehensive website security solutions designed to identify vulnerabilities, strengthen protection, and maintain reliable online operations.
From security assessments, malware protection, SSL implementation, secure hosting environments, and website monitoring to recovery support after security incidents, Chromeis helps organizations build stronger defenses against common website threats.
The focus is on preventing problems before they affect customers and business operations.
Final Thought
Website security is not something businesses can ignore until an attack happens.
Small weaknesses can create major problems if they are not addressed.
By understanding common vulnerabilities and applying consistent security practices, businesses can protect their websites, customer information, and online reputation.
A secure website creates confidence for both businesses and the people who rely on them.
Frequently Asked Questions (FAQs)
1. What are the most common website security vulnerabilities?
Common website security vulnerabilities include outdated software, weak passwords, insecure plugins, poor access controls, incorrect server configurations, and missing security updates. These weaknesses can allow attackers to gain unauthorized access, steal information, or compromise website functionality.
2. How can businesses protect their websites from cyber attacks?
Businesses can improve website protection by regularly updating software, enabling multi-factor authentication, installing SSL certificates, restricting user permissions, performing security scans, and maintaining reliable backups. Combining these measures creates multiple layers of protection against common threats.
3. Can an SSL certificate protect a website from hacking?
An SSL certificate helps encrypt information transmitted between a visitor’s browser and the website server. However, it does not prevent malware infections, weak password attacks, or software vulnerabilities. Businesses need additional security measures to protect their websites effectively.
4. What should a business do if its website gets hacked?
A business should restrict unauthorized access, preserve relevant evidence, identify compromised files and accounts, remove malicious code, and address the vulnerability that caused the attack. After cleaning the website, it should reset affected credentials, restore verified backups if necessary, and continue monitoring for suspicious activity.
5. How often should businesses perform website security checks?
Businesses should monitor their websites continuously where possible and perform regular security reviews. Software updates should be applied promptly based on their severity, while vulnerability scans, backup checks, and access reviews should follow a defined schedule. Websites handling sensitive information or frequent transactions may require more intensive monitoring.
Similar Post
How SSL Encryption Builds Trust and Protects Customer Data
People share information online every day. They sign in
Essential Website Security Measures to Protect Your Online Presence
A website is often the first place customers interact